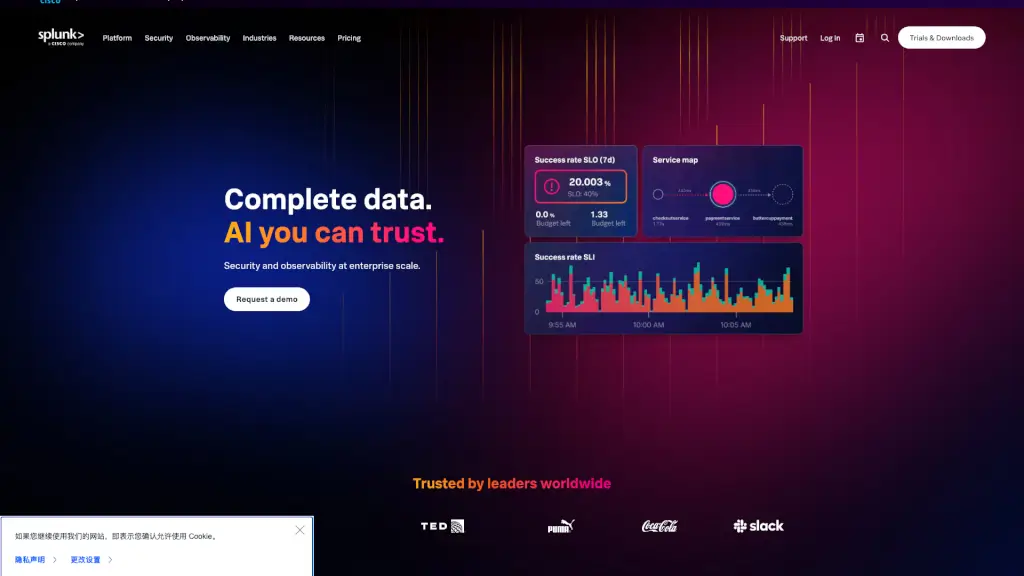
Splunk delivers unified security and observability at enterprise scale, using AI and trusted data to prevent disruptions, accelerate response, and build digital resilience.

Social Media:
Splunk

Splunk Product Information

What is Splunk?

Splunk is a powerful unified security and observability platform that helps organizations stay resilient in today’s fast-moving digital world. By bringing together machine data from across your entire tech environment—servers, apps, networks, cloud services, and more—it gives teams real-time visibility to detect threats, troubleshoot issues, and prevent disruptions before they impact customers.

Originally known for its log analysis capabilities, Splunk has evolved into an AI-powered platform that supports both security operations (SecOps) and IT observability at enterprise scale. Whether you're a SOC analyst hunting advanced threats or an SRE optimizing application performance, Splunk provides a single source of truth backed by trusted data and contextual intelligence.

Now part of Cisco, Splunk continues to lead the industry—recognized as an 11-time Gartner Magic Quadrant Leader for SIEM and a 3-time Leader for Observability Platforms—helping global brands like Carrefour, Singapore Airlines, and Progressive Insurance respond faster, reduce downtime, and drive digital transformation with confidence.

What are the features of Splunk?

  • Unified Data Platform
    Ingest, index, and analyze petabytes of machine data from any source—logs, metrics, traces, network packets—with built-in support for OpenTelemetry.
  • AI-Powered Security (Agentic SOC)
    Leverage AI and Cisco Talos threat intelligence to automate threat detection, investigation, and response—cutting response times by up to 3x.
  • Observability with AIOps
    Use Splunk IT Service Intelligence (ITSI) and AppDynamics to monitor service health, predict outages, and reduce alert noise across cloud and on-prem environments.
  • Advanced Threat Detection
    Combine UEBA, behavioral analytics, and risk scoring to uncover insider threats, lateral movement, and “living off the land” attacks.
  • Compliance Automation
    Streamline audits and reporting for standards like PCI DSS, HIPAA, and GDPR with pre-built content and real-time dashboards.
  • 2000+ Integrations
    Extend functionality via Splunkbase with apps for cloud platforms, SaaS tools, IoT devices, and operational technology (OT).
  • Fraud & Financial Crime Prevention
    Detect suspicious patterns in real time using customizable detection rules and cross-domain correlation.

What are the use cases of Splunk?

  • Accelerate SOC productivity
    by automating repetitive tasks with SOAR and reducing manual investigations through AI-driven insights.
  • Reduce mean time to resolution (MTTR)
    by 10x using end-to-end observability across microservices, third-party APIs, and backend systems.
  • Ensure compliance
    with automated evidence collection and audit-ready reports for regulatory frameworks.
  • Prevent revenue loss
    by detecting fraud in e-commerce or financial transactions before it escalates.
  • Optimize cloud costs and performance
    by correlating infrastructure metrics with business KPIs to identify waste and bottlenecks.
  • Improve customer experience
    by proactively identifying and fixing issues affecting end-user journeys—before users complain.
  • Modernize legacy IT
    by unifying monitoring from disparate tools into a single pane of glass, cutting licensing costs by up to 30%.

How to use Splunk?

  • Start with a free trial or product tour on Splunk’s website to explore core capabilities without commitment.
  • Install Universal Forwarders or OpenTelemetry agents to begin streaming logs, metrics, and traces into your Splunk deployment.
  • Use pre-built content packs from Splunkbase (like detection rules for SIEM or dashboards for AWS) to accelerate time-to-value.
  • Enable AI features like Anomaly Detection or Attack Analyzer directly within Splunk Enterprise Security or Observability Cloud.
  • Integrate with your ticketing system (e.g., ServiceNow) to auto-create incidents and reduce manual handoffs.
  • Leverage Splunk Lantern or community forums to find best practices, troubleshooting tips, and user-contributed solutions.
Do you like this tool?

Upvote to help others discover it!

Splunk Alternatives

New Relic

New Relic

New Relic delivers AI-powered observability that predicts, explains, and fixes issues across your full stack—tying technical performance directly to business outcomes.

US
36.38%
1.4M
0
Dynatrace

Dynatrace

Dynatrace delivers AI-powered observability that turns data into autonomous actions, helping teams build, secure, and run better software faster.

US
35.52%
1.5M
0
LogicMonitor

LogicMonitor

LogicMonitor is a hybrid observability platform that simplifies IT monitoring with AI-driven insights, multi-cloud support, and seamless integrations.

US
55.60%
414.1K
0
Elastic Stack

Elastic Stack

Elastic is a versatile search AI platform that delivers fast, relevant results and enhances security, observability, and more, driving business outcomes.

US
34.10%
1.1M
0
Abstract Security

Abstract Security

Abstract Security streamlines security data, cuts noise, and boosts threat detection—all with no-code ease. Perfect for teams tired of SIEM complexity.

US
100.00%
3.5K
0
Dash0

Dash0

Dash0 delivers OpenTelemetry-native observability with unified logs, metrics, and traces, transparent pricing, and zero vendor lock-in—so teams get deep insights fast without complexity.

DE
22.32%
216.0K
0
Intezer

Intezer

Intezer’s Autonomous SOC Platform uses AI to automate alert triage, investigation, and remediation, reducing false positives and speeding up response times. It’s a must-have for modern security teams.

US
19.07%
41.6K
0
Radiant Security

Radiant Security

Radiant Security is an AI-powered SOC co-pilot that boosts analyst productivity, detects real attacks, and improves response times, all while maximizing your existing security investments.

US
38.56%
10.2K
0

Splunk Related Other Categories

Splunk Traffic Analysis

Website traffic estimates for splunk.com. Visits are not unique users or product usage.

💡 Insights

📈
High Traffic
Over 1M monthly visits. Widely recognized and stable choice.
⚠️
Slight Decline
Traffic has slightly decreased recently.
👍
Good Experience
Bounce rate of 49%. Users are willing to explore features.
  • Monthly Visits

    1.07M

  • Bounce Rate

    49.13%

  • Pages Per Visit

    3.31

  • Visit Duration

    00:02:42

  • Global Rank

    48731

  • Country Rank

    25303

Visits Over Time

Traffic Sources

Search Organic37.40%
Direct29.16%
Referrals22.11%
Search Paid4.35%
Social Organic2.73%
Gen Ai1.45%
Mail1.25%
Display Ads1.18%
Social Paid0.37%
Affiliate0.00%

Top Keywords

1
splunk
CPC$3.15
35.00KTraffic
2
caesar cipher
CPC$3.89
2.08KTraffic
3
splunk download
CPC$15.68
1.86KTraffic
4
splunbk
CPC$4.94
1.46KTraffic
5
splunk clean-dispatch examples
1.46KTraffic

Top Regions

RegionPercentage
United States
United States
38.09%
India
India
14.87%
Poland
Poland
3.10%
Australia
Australia
2.73%
United Kingdom
United Kingdom
2.10%
Low
High

Powered by SimilarWeb

Splunk FAQ

What is Splunk used for?

Splunk is used for security monitoring (SIEM/SOAR), IT observability, application performance management (APM), compliance auditing, and fraud detection—all powered by a unified data platform that turns machine data into actionable insights.

Is Splunk a SIEM tool?

Yes, Splunk Enterprise Security is a market-leading SIEM that’s been named a Gartner Magic Quadrant Leader 11 times. But Splunk goes beyond traditional SIEM by also offering deep observability, AIOps, and automation capabilities in one platform.

How does Splunk help with observability?

Splunk provides real-time visibility across any stack—cloud, on-prem, or hybrid—using metrics, logs, and traces. With AI-driven features like alert noise reduction and service health scoring, teams can quickly pinpoint root causes and prevent outages.

Can Splunk integrate with other tools?

Absolutely! Splunk supports over 2,000 integrations via Splunkbase, including cloud providers (AWS, Azure, GCP), SaaS apps, networking gear, and DevOps tools—all with native OpenTelemetry support for easy instrumentation.

Is Splunk now part of Cisco?

Yes, Splunk is now a Cisco company, which enhances its threat intelligence with Cisco Talos and expands its ability to deliver end-to-end security and network resilience at scale.

Does Splunk support compliance requirements like GDPR or HIPAA?

Yes, Splunk offers built-in compliance content and dashboards that automate monitoring and reporting for major regulations including PCI DSS, HIPAA, GDPR, and SOX—helping teams prove adherence during audits.

How does AI work in Splunk?

Splunk uses trusted, context-aware AI to enhance security and observability workflows—like predicting incidents before they happen, auto-correlating alerts, and summarizing complex investigations—so teams can act faster with confidence.

Splunk Reviews

0
0 Reviews
Sign Into leave a review

Recent Reviews

No reviews yet

Splunk Embed

Use website badges to drive community support for SeekTool.ai. They are easy to embed in your homepage or footer.

Light
Dark
Splunk - Featured on SeekTool.aiSplunk - Featured on SeekTool.ai
How to install?